DK AI Shield shield symbolDK AI ShieldFINANCIAL & DIGITAL ASSET SECURITY

DAS architecture

Introduces the software processing flow and hardware installation configuration

Contact DAS ↗
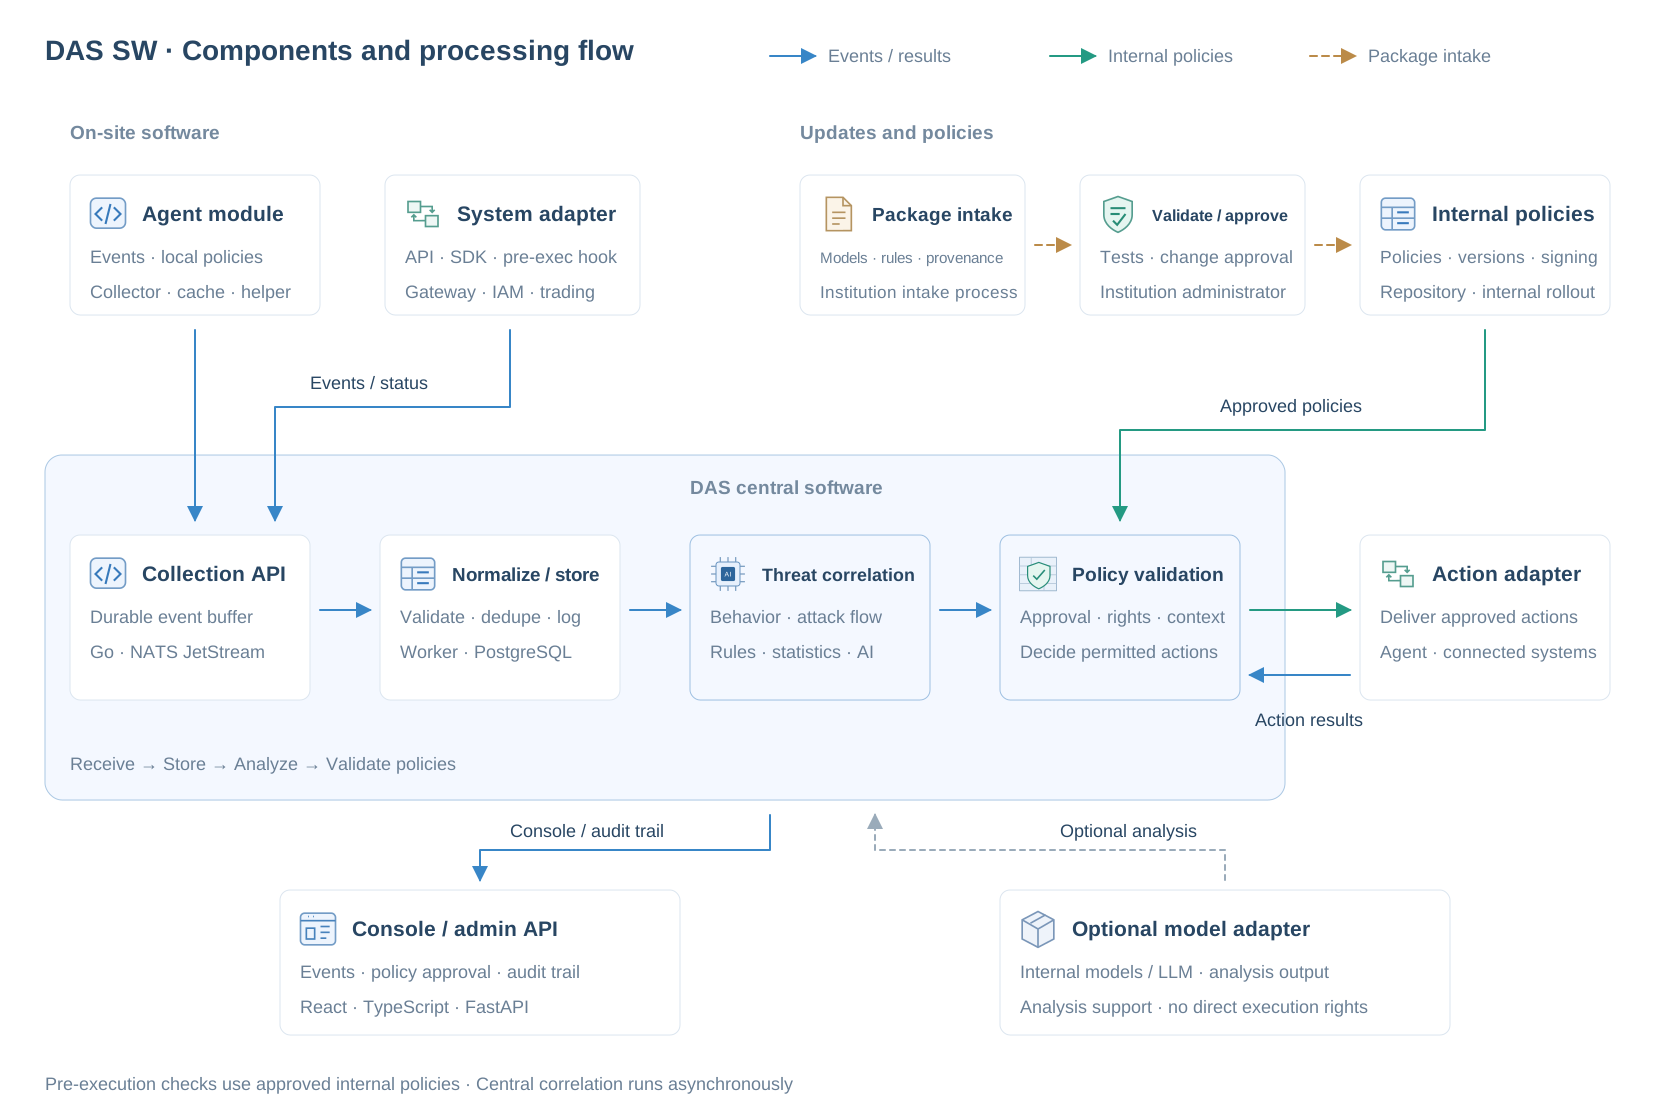
DAS SW software configuration and processing flow. The Agent module and system adapter forward events to the collection API. NATS JetStream and PostgreSQL, threat correlation analysis, independent policy validation, and execution adapters are connected. Place AI images and policy verification images in the same module size. Control web/management API and selection model adapter are linked.
Server Agent · Gateway · Trading API
  1. 01

    event collection

    Go Collection API · NATS JetStream

  2. 02

    Normalization/Storage

    Duplicate handling PostgreSQL

  3. 03

    Threat correlation analysis

    Rules · Statistics · AI

  4. 04

    Independent Policy Verification

    Check approval scope and work conditions

  5. 05

    on-site enforcement

    Agent · Gateway · Transaction execution department

Control and audit React · FastAPIanalysis assistant Select Model/LLMupdate Verification, approval, signature distribution

Verification with approved policies is performed in the field, and central correlation analysis is performed asynchronously

Technical composition and detailed flow
control React · TypeScriptManagement/Analysis FastAPI · PythonAgent·Collection·Policy GoMessage/Save NATS JetStream · PostgreSQL
Software processing flowCollection → Storage → Analysis → Policy Verification → Execution Confirmation
01 · AGENT & CONNECTOR

On-site collection and system connection

Go Agent collects server events Link events from the Gateway, Authentication, and Transaction APIs with pre-execution verification results

Go AgentLog · API · SDK
↓ Event delivery
02 · INGESTION & STORAGE

Collection, normalization, event storage

Events are received using the Go collection API and NATS JetStream Workers clean up duplicates and formats and write to PostgreSQL

NATS JetStreamPostgreSQL
↓ Events subject to analysis
03 · ANALYSIS & POLICY

Threat analysis and independent policy verification

Rules, statistics, and AI analyze the context of behavior and attack flow An independent policy engine determines actions by checking the approval scope and business conditions

Python analysisGo policy engine
↓ Approved policies/orders↑ Execution result
04 · ENFORCEMENT

Check actual execution and results

The policy is applied at the verification point before execution of the server's restriction helper, gateway, and transaction app Reconfirm the results of the actions and leave an audit history

MANAGEMENT & CONSOLE

Control screen/management API

Check asset, threat, policy, and action history with React·TypeScript control and FastAPI management API Apply role-specific access rights and operator approval

OPTIONAL MODEL ADAPTER

Select model linkage

Associate an internal model·LLM or an approved external LLM as an analytical assistant The analysis results of the model and the actual execution authority are separated

All components
01

access channel

Access path for customer/business system

Mobile/Internet Banking

Customer access and authentication requests

Virtual asset service

Exchange/wallet access

External/Affiliate API

Link service request

Operator access

Business/Management Console

Service Request
02

Existing security environment

Connect to existing infrastructure

Firewall/IPS

network security

WAF

Web Request Protection

API Gateway

API access path

DLP/Transmission Control

Information Export Path

03

financial business system

Business and assets to protect

Certification/Customer Information

Account/Permission/Work Context

Transaction/Payment API

Remittance/withdrawal/approval request

Wallet/Signature System

Virtual asset/signature verification

Ledger/Business System

Transaction ledger/internal work

event collectionDeliver action, log, and transaction events through server agent and system integration

Central analysis/policy/control

DAS Core

event collection

Event Collector

Log/behavior/transaction event connection

AI correlation analysis

AI Threat Analysis Engine

Analysis of known and modified attack signs and likelihood of progression

Independent Policy Verification

Policy Engine

Verification of approval scope and execution conditions

Transaction Protection

Transaction Guard

Comparison of transaction requests and approvals

Account/session protection

Identity Guard

Check access, terminal, and session context

data protection

Data Guard

Confirm inquiry/file/external transmission

network connection

Gateway Connector

Connect to existing firewall/gateway

Overview

Management Console

Check event/policy/action history

Attack flow/spread prediction

Threat Graph

Estimation of attack stages and possible spread routes

Communicate approved policiesSelectively applied to necessary execution points according to verified conditions
04

optional response point

Respond according to approval conditions for each task

Server Agent

Server behavior and information export control

Gateway integration

Restrict unauthorized access/requests

Transaction API integration

Check approval conditions and hold execution

Deployment configuration

Server Agent

business server

Gateway

network connection

Trading API

Link execution conditions

central server

Analysis/Policy Management

operator console

Control, review, history

event collection Apply approved policies AI analyzes threats and an independent policy engine verifies approval conditions and execution requests Response is performed by server Agent, Gateway, and Transaction API
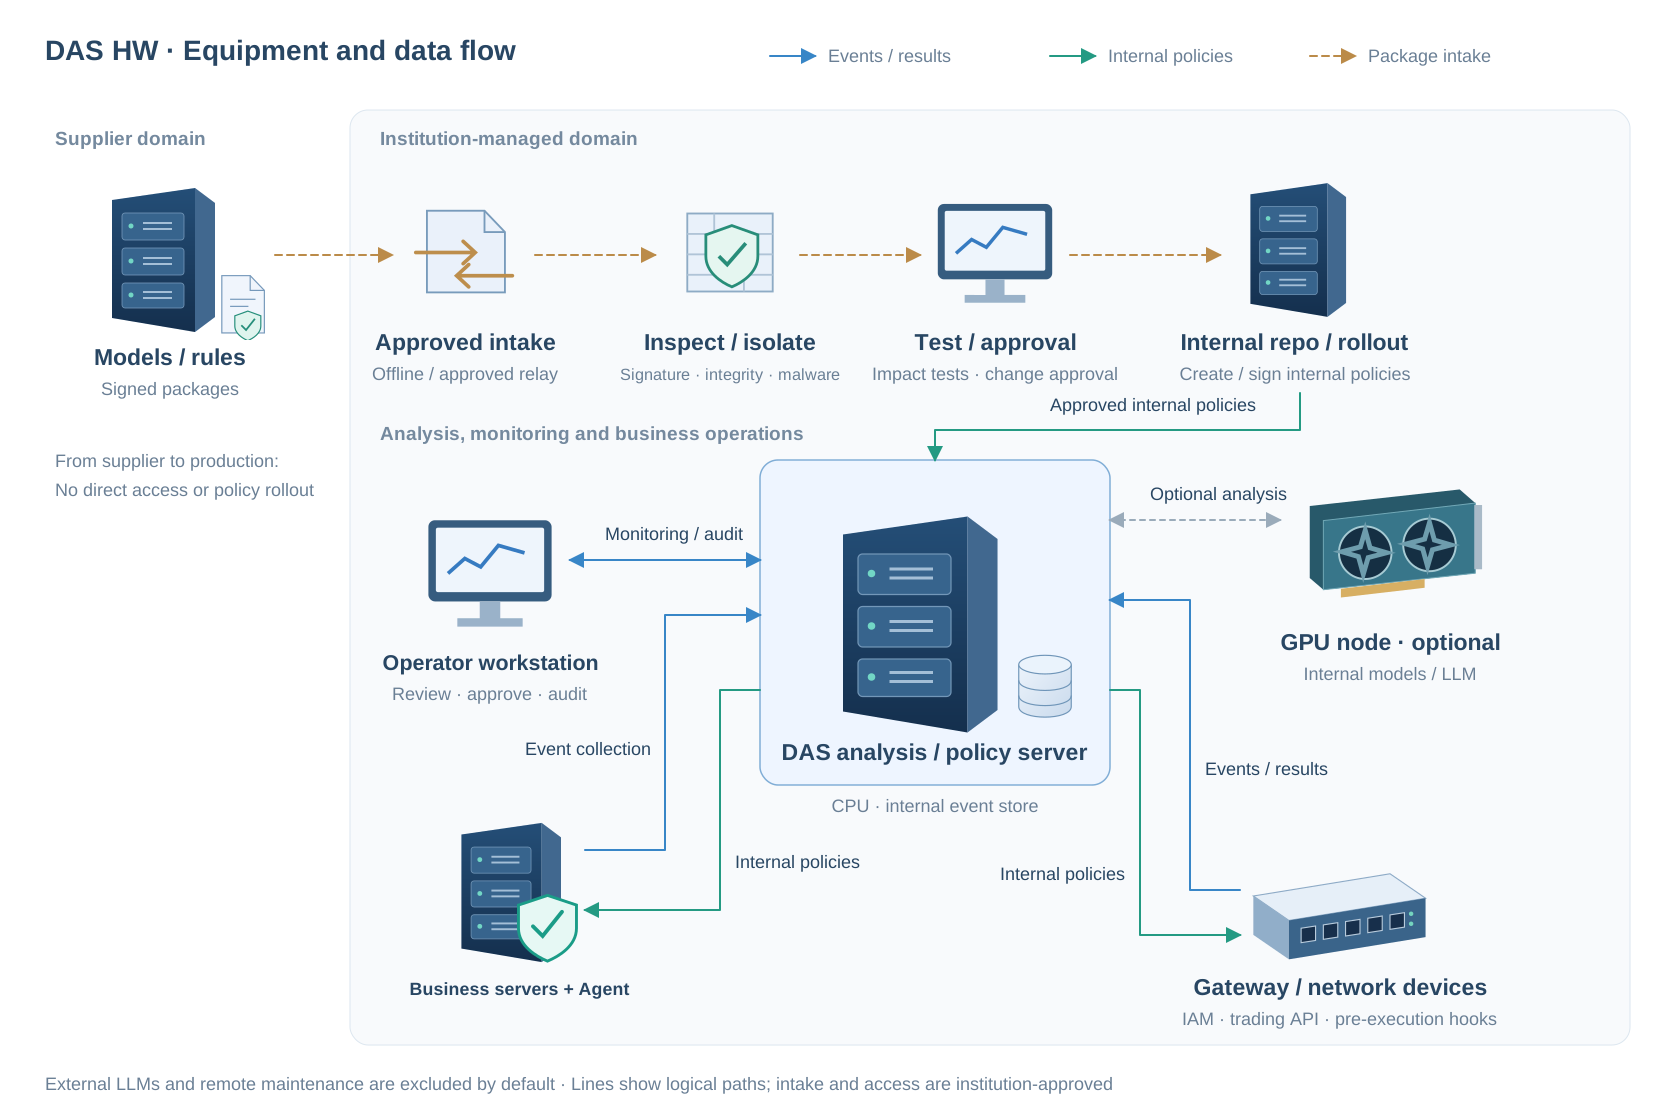
DAS HW equipment and data flow. The financial institution imports the signature package provided by the supplier through a controlled route and inspects, tests, and approves it. The institution's internal storage and distribution system transmits policies to the DAS analysis and policy server. The business server Agent and Gateway deliver events and execution results and apply approved internal policies. GPU is an optional configuration, and external LLM/remote maintenance is excluded from the default configuration.

customer care area Internal network / dedicated cloud

business serverServer Agent
existing systemGateway · Authentication · Transaction
↓ Event collection↑ Approved policy
CPU

DAS analysis/control server

Collection · Analysis · Policy · Storage

GPU nodeSelection Configuration · Internal Model · LLM

outside the customer network

Institutional approval/internal distributionPackage import → Agency verification/approval → Internal distribution
External LLM API selectAssist analysis with approved incident information

The supplier provides the package, the agency verifies and approves it, and then distributes the policy internally

Installation scope and update method
customer care areaInternal network and customer-only cloud
01 · Installation on business server

Server Agent

Server behavior is collected from supported OSs and controlled limitedly according to approved policies

Linux · WindowsPhysical server · VM

UNIX·Embedded consists of log·SDK·network linkage depending on the scope of support

02 · Link with existing system

Gateway · Authentication · Transaction API

Connects to existing security equipment, wallet and transaction systems Actual request limits and transaction holds are handled by the execution point of the system

↓ Event collection↑ Approved policy
03 · Placed on a separate server

DAS analysis/policy/control server

It is responsible for CPU-based rules, statistics, and lightweight AI analysis, event storage, independent policy verification, and operator control

Customer-only server/VMCustomer baseline internal management
Selection · Customer Internal Expansion

GPU analytics server

Add if advanced model/internal LLM is required It is separated from basic policy verification and enforcement

outside the customer networkUpdates and selection analysis
Supplier → Customer

Research/update server

Provides a signature package of rules and models improved by the supplier with public, synthesized, and approved data It is distributed internally after the institution approves incoming inspection, testing, and changes

Upon selection/customer approval

External LLM API

Excluded from the default configuration When separately introduced, the agency reviews the applicable section, transmission information, contract, and access control Direct execution permission is not granted

Defense algorithm update

Only validated changes in stages

The customer's normal business baseline and applicable policies are maintained in the customer management area

  1. 01Research/EvaluationImproved rules and models
  2. 02signature packageVersion/integrity check
  3. 03Customer Verification/ApprovalSee the impact in observation mode
  4. 04Phased applicationRevert to the approved version

Server Configuration DAS is deployed on a physical server/VM inside the customer or on a cloud dedicated to the customer The event store can be separated from the analytics server at scale GPU devices and internal LLM are optional configurations

Work system connection It combines server agent, log collection, gateway API, and integration before transaction execution Transaction suspension, additional authentication, and information export restrictions are applied within the scope of the linked system's authority and approved policies

External connection and network separation External LLM connections are excluded from the basic configuration, and are subject to separate review and approval by the institution when introduced The network separation environment is configured to internally distribute signature packages after the agency imports, verifies, and approves them, and maintains the basic policy verification and enforcement path without GPU or external API

Application by environment The installation method and scope of collection and control are determined according to the operating system, version, permissions, network, and linking API For UNIX/embedded, etc., it is determined whether Agent installation or log/SDK linkage is possible

DAS · DK AI SHIELD

Contact DAS

Please tell us which system you want to link to and what security features are required

Contact DAS ↗